Skip to content
Resource_Centre_600x320

Practical resources for navigating compliance, testing, and global market access.

Blog_writing_600x320

Expert insights on compliance, testing, certification, and evolving regulatory requirements.

Certificate_Finder_600x320

Verify certificate authenticity and certification status through Nemko’s online platform.

Locations_600x320

Find Nemko locations worldwide and connect with local experts for testing, certification, compliance, and global market access services.

busy-office-work-space-cyber-security-people-1560x1060

On-demand Webinar: Protecting your company’s assets: Risk Management and ISO 27001

Are you doing everything you can to protect your company's assets like financial information, intellectual property, and employee details? The information security management system standard, ISO/IEC 27001:2017, is designed to specify the requirements for implementing security controls within an organization. This standard directly addresses the risks and mitigations necessary for your business to operate in an ever-increasing environment of cyberattacks.

Join us as we team up with Mark Jackson from Pacific Quality Solutions to present you with a webinar on protecting your company's assets: Risk Management and ISO 27001. Learn how to preserve information confidentiality, integrity, and availability by applying a risk management process to assure interested parties that risks are effectively managed. 

Webinar presenter

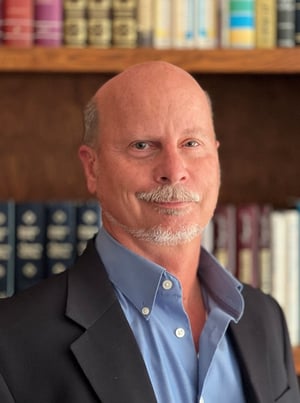
Mark Jackson
Mark Jackson Principal Consultant and Certification Body Auditor

Mark Jackson has 30 years of quality management experience in global, multi-site manufacturing organizations throughout the United States, Europe, Asia, South America, and Africa. He has experience in several industries, including Medical Devices, Industrial, DoD, telecommunications, and Commercial. He has developed cross-functional teams focused on operational excellence throughout small and large business organizations. Mark is a consultant and Certification Body Auditor for ISO 13485:2016, ISO 9001:2015 and ISO 27001:2013.